No products in the cart.
- Published: Oct 22, 2026 | Updated: Oct 22, 2026

Understanding PHP2Shell: Technical Analysis and Patching CVE-2026-109618 & CVE-2026-109619
Table of Contents
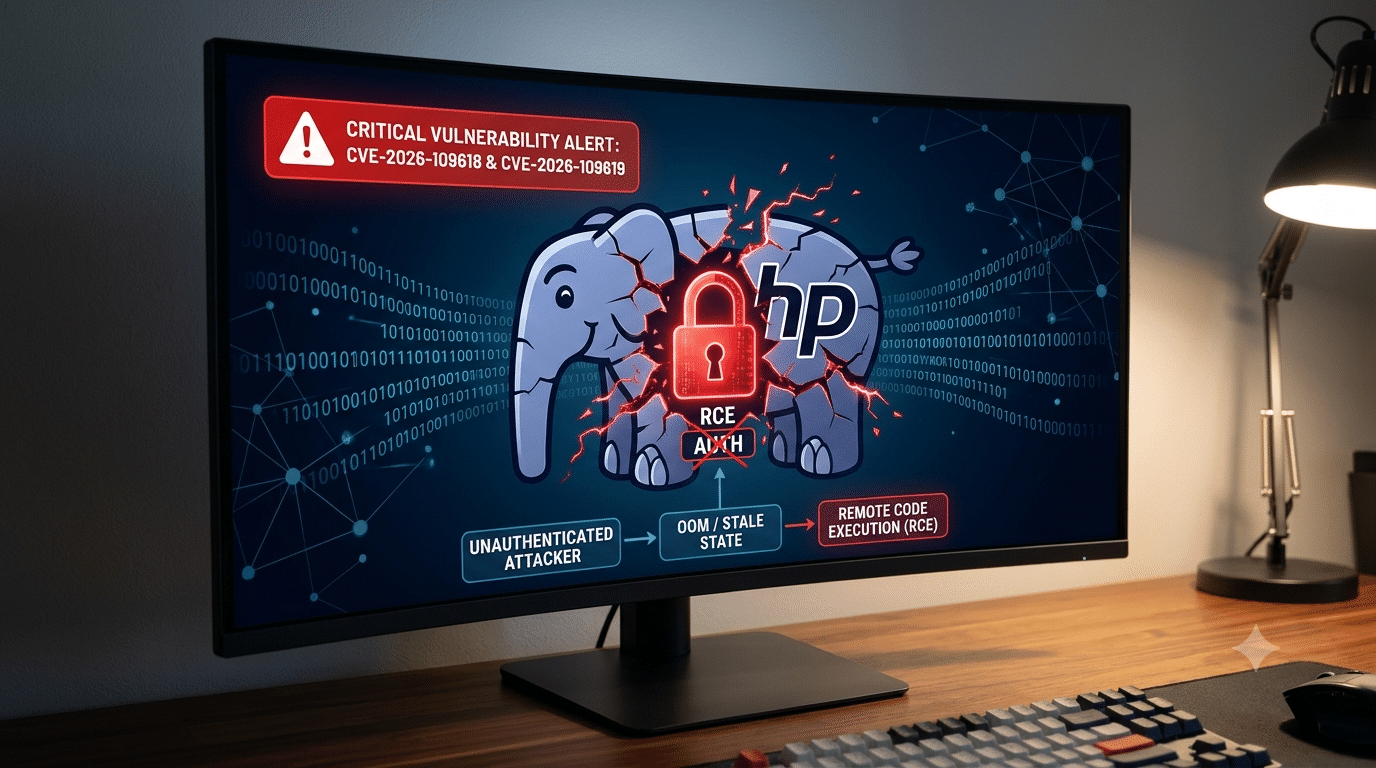
A pair of critical Remote Code Execution (RCE) vulnerabilities in core PHP—collectively known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619)—have sent shockwaves through the web infrastructure landscape. With a CVSS score of 9.2, these flaws allow unauthenticated attackers to execute arbitrary code on vulnerable servers without needing valid user credentials or prior access.
Because PHP powers roughly 75% of websites globally (including platforms like WordPress, Drupal, Magento, and thousands of custom Enterprise stacks), immediate remediation is vital.
This article explores the technical mechanics of PHP2Shell, its impact, and step-by-step mitigation strategies.
What Makes PHP2Shell So Dangerous?
Most application-layer RCE vulnerabilities stem from flawed application code (e.g., unsafe deserialization or unauthenticated file uploads). PHP2Shell is different: it is a vulnerability within the PHP language interpreter itself.
Key factors amplifying the risk:
Pre-Authentication Exploitation: The vulnerability triggers during PHP’s internal request parsing and cleanup phases—before your web framework or security logic executes.
Broad Environment Impact: It affects virtually all major PHP deployment architectures, including PHP-FPM,
mod_php,php-cgi, FrankenPHP, and LiteSpeed.Wide Version Range: Impacted versions span from PHP 5.4 all the way up through early builds of PHP 8.5.
The Technical Root Cause: Memory Management Failures
PHP2Shell comprises two distinct underlying flaws in PHP’s C-level memory and request state management:
1. Out-of-Memory Handling Flaw (CVE-2026-109618)
When a PHP worker thread encounters an Out-of-Memory (OOM) error while handling abnormally large or complex request payloads (such as excessive headers or multipart file data), it triggers an emergency cleanup routine.
During this emergency teardown, the Zend Engine misinterprets partially initialized internal data structures as fully formed objects. As it attempts to free these pointers, it creates a Use-After-Free (UAF) or heap memory corruption scenario, allowing an attacker to manipulate pointer addresses and hijack control flow.
2. Request State Persistence / Stale Pointer Reuse (CVE-2026-109619)
In persistent worker models (like PHP-FPM or FastCGI), PHP reuses worker processes across multiple HTTP requests to optimize performance.
Under specific abnormal termination conditions, request-bound memory state is freed, but reference pointers to those allocations remain intact in global execution context structures. When a subsequent request hits the same worker process, it inherits this “stale state.” A widely recognized weaponization path leverages PHP’s default session upload progress feature (session.upload_progress), enabling attackers to craft secondary payloads that read or execute corrupted memory references.
How to Test and Detect Vulnerable Assets
1. Check PHP Interpreter Version
Run the following on your web/application servers:
php -v
Vulnerable Releases:
PHP 8.5.x prior to 8.5.12
PHP 8.4.x prior to 8.4.27
PHP 8.3.x prior to 8.3.36
PHP 8.2.x prior to 8.2.35
All EOL versions (PHP 5.x, 7.x, 8.0, 8.1) unless using active vendor-backported packages (e.g., RedHat, Ubuntu LTS, RHEL/Debian security repos).
2. Log Analysis & Indicators of Compromise (IoCs)
Monitor your web server and PHP-FPM error logs for abnormal patterns:
Frequent PHP process crashes (
SIGSEGVorSIGABRT) accompanied by OOM errors.Unusually high volumes of
POSTrequests sending largeContent-Lengthheaders or deeply nested multipart form fields.Suspicious file creations in system temporary directories (
/tmp,/var/tmp).
Remediation & Patching Guide
Step 1: Update PHP Packages Immediately
Upgrade to the patched releases provided by the official PHP team or your Linux distribution vendor:
PHP 8.5: Upgrade to 8.5.12+
PHP 8.4: Upgrade to 8.4.27+
PHP 8.3: Upgrade to 8.3.36+
PHP 8.2: Upgrade to 8.2.35+
Example for Ubuntu/Debian systems:
sudo apt update && sudo apt install --only-upgrade php-fpm php-cli
Step 2: Restart Web Server & PHP Service Workers (CRITICAL)
Updating files on disk is not enough—running PHP worker processes keep the vulnerable code loaded in RAM.
# Systemd restart commands
sudo systemctl restart php8.3-fpm   # Adjust version as needed
sudo systemctl restart nginx        # Or apache2 / litespeed
Temporary Workarounds (If Immediate Patching Is Not Possible)
If your environment relies on legacy PHP versions that cannot be immediately upgraded, apply these defense-in-depth measures:
1. Disable Session Upload Progress
In your php.ini file, set:
session.upload_progress.enabled = 0
After changing php.ini, restart PHP-FPM/Web Server.
2. Restrict Request Body Sizes at the Reverse Proxy Level
Prevent attackers from sending memory-exhausting payloads by enforcing strict payload size limits in Nginx, Apache, or Cloudflare/WAF layers.
Nginx Example (/etc/nginx/nginx.conf):
Nginx
client_max_body_size 10M;
client_header_buffer_size 1k;
large_client_header_buffers 4 4k;
Conclusion
PHP2Shell underscores the critical necessity of runtime-level patching and defense-in-depth strategies. Web Application Firewalls (WAFs) and code security scans can help mitigate threats, but upgrading the underlying runtime remains the only permanent defense.
Take time today to audit your server infrastructure, apply security updates, and verify that running processes have been fully restarted.
Found this helpful? Share it with your Dev, SecOps, and Systems Engineering teams!